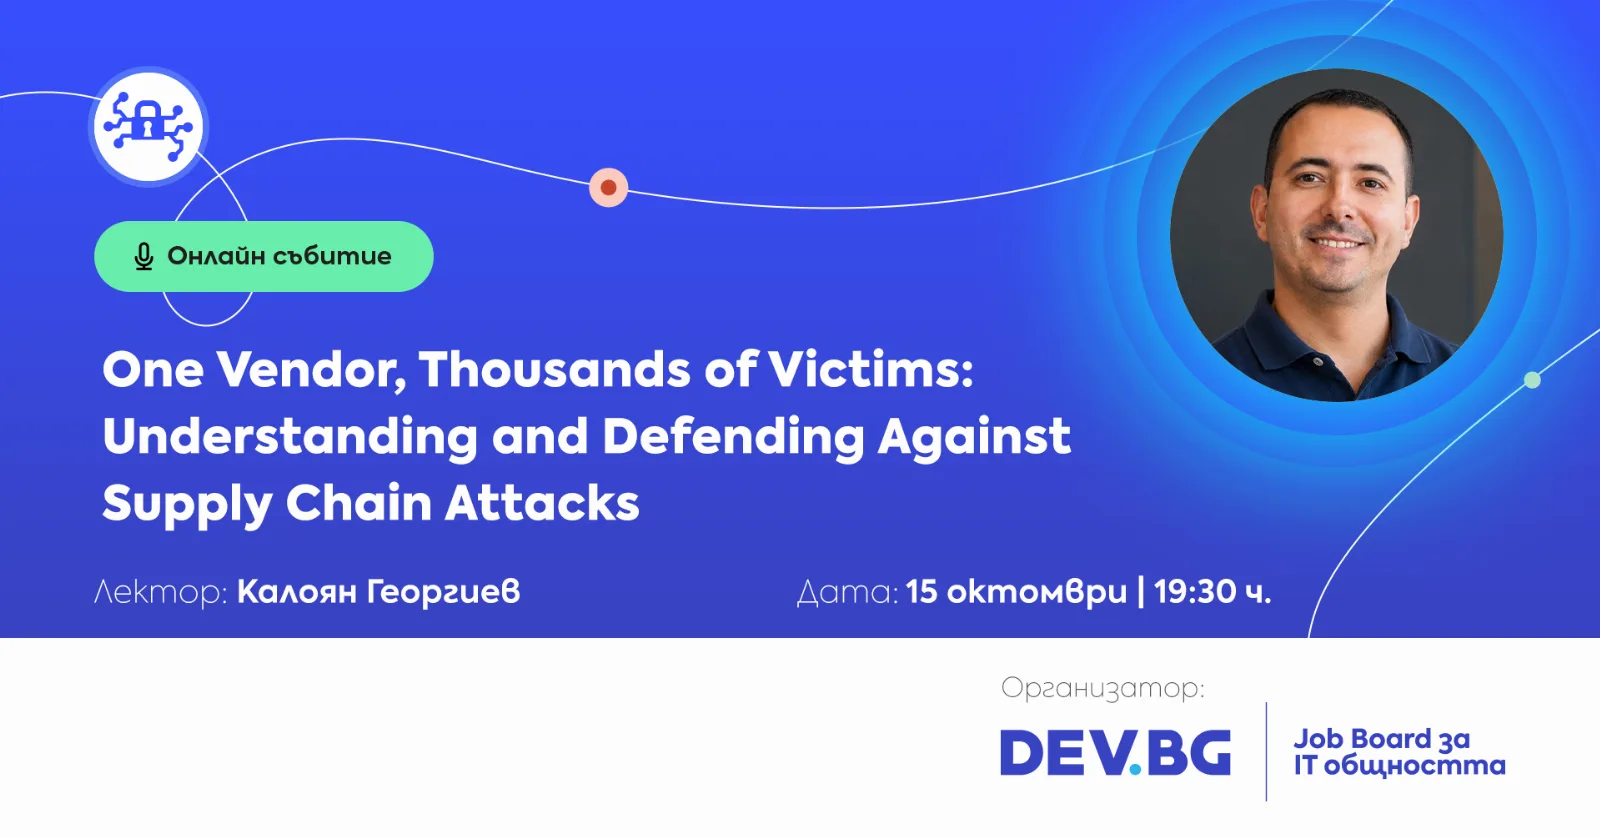
One Vendor, Thousands of Victims: Understanding and Defending Against Supply Chain Attacks
Това събитие е част от потребителската група Cyber Security.
ПРОГРАМА:
>>> What is a supply chain attack and why it scales so well
>>> SolarWinds: anatomy of an attack that reached ~18,000 organizations through a single update
>>> Poisoned dependencies: typosquatting, dependency confusion and hijacked maintainer accounts (npm, PyPI, Maven)
>>> Compromised updates and build pipelines: when the trusted channel becomes the attack vector (3CX, XZ Utils, CI/CD)
>>> Why trusting vendors is a risk: transitive dependencies and hidden blind spots
>>> SBOM (Software Bill of Materials): knowing what actually runs in production
>>> How companies defend: dependency pinning, artifact signing & provenance (Sigstore, SLSA), least privilege and vendor risk management
>>> Practical lessons for enterprise teams: what to do on Monday morning
>>> Q&A част
Събитието е безплатно, но със задължителна предварителна регистрация.
ПОТРЕБИТЕЛСКА ГРУПА: Cyber Security
Събитието е част от потребителската група за Cyber Security. Всеки месец организираме събития на тема свързана със Cyber Security. За да не изпускате интересна информация по темата – абонирайте се.
ОРГАНИЗАТОР: DEV.BG е специализиран Job Board за IT обяви.
Cyber Security обяви: Ако си търсиш работа като Cyber Security специалист, разгледай свободните позиции тук.
КОГА: 15.10.2026 г. от 19:30 ч.
Очакваме ви!
Kilde: dev.bg